
Abstract:
French cryptocurrency hardware wallet maker Ledger is investigating a security incident involving malicious modification of its devices. Some wallets were found to have hidden monitoring components installed, and blockchain researchers estimate that more than $90 million in related crypto assets have been stolen. The investigation initially focused on Malaysian cryptocurrency retailer CryptoBilis, but other sales channels have now been identified that may contain infected devices.
Malicious hardware can steal sensitive information and bypass the wallet center security chip
Ledger stated that an organized criminal group installed hidden components inside some hardware wallets, which may allow attackers to obtain users' digital assets without directly cracking the device's core security chip.
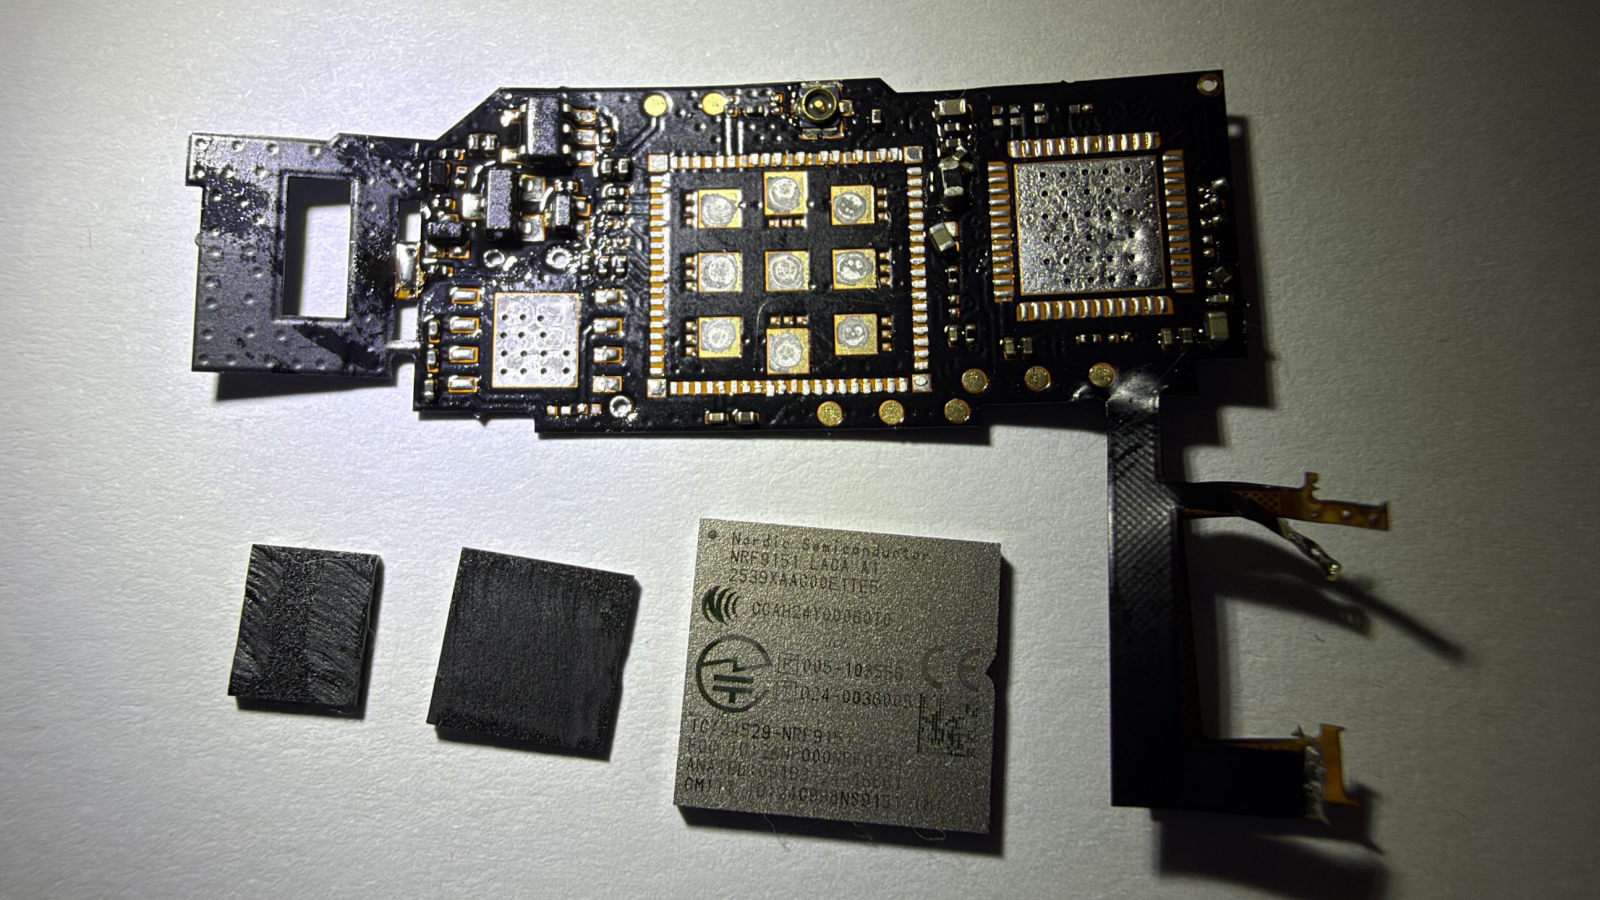
Independent security researchers pointed out that related devices may intercept sensitive information through modified display connection components, and then use cellular communication modules to transmit the information to attackers.
Since October 9, CryptoBilis customers have successively reported the loss of digital assets, and the retailer subsequently temporarily closed its physical store in Kuala Lumpur. Ledger said it is cooperating with local law enforcement in the investigation.
Singapore sales equipment also found abnormalities, and the scope of the impact may be expanded
Investigators also found modified display connectors, cellular communication chips and SIM cards in a Ledger Flex wallet purchased from Singapore Changi Airport.
This discovery means that infected devices may have entered normal retail channels in multiple countries.
Ledger is still investigating the scope of the attack and has not announced the total number of affected devices.
This incident also exposed the security risks in the hardware wallet supply chain: even if the device itself uses an independent security chip, user assets may still be at risk if it is physically modified during sales or circulation.
Comments