
Abstract:
According to CCTV News, recent incidents of user access requests abnormally jumping to gambling websites have occurred in many provinces in China, causing serious harm to the property security and normal Internet rights of the people. After analysis, the attackers used China's overseas autonomous domain AS 402425 to carry out attacks mainly by declaring false routes and tampering with domain name resolution data. The scope of harm is wide. The relevant investigation results are hereby announced to provide reference for relevant countries, units and netizens around the world to effectively discover and prevent such attacks.
1. Network attack process
(1) Hijacking traffic by announcing false routes. The attacker registered false source address prefixes and false autonomous domain sets in the Internet routing registry, used the autonomous domains under its control to publish false source address prefixes and false short paths, and hijacked some traffic within China.
(2) Tampering with DNS resolution data in hijacked traffic. After attackers hijack the traffic, they tamper with the DNS resolution data in it. There are two main methods: one is to directly modify the DNS resolution value to the gambling website address; the other is to point the DNS resolution value to the malicious DNS server address. When the user requests domain name resolution from the malicious DNS server, the gambling website address will be returned.
2. Network attack location
Through technical measurements, it was confirmed that the domain name tampering occurred in AS 402425, an autonomous domain outside China. This autonomous domain was registered by the American company QOREXA LABS with ARIN, the American Internet Number Registration Authority, on April 9, 2026. The company's official website shows that it operates Bitcoin-related businesses.
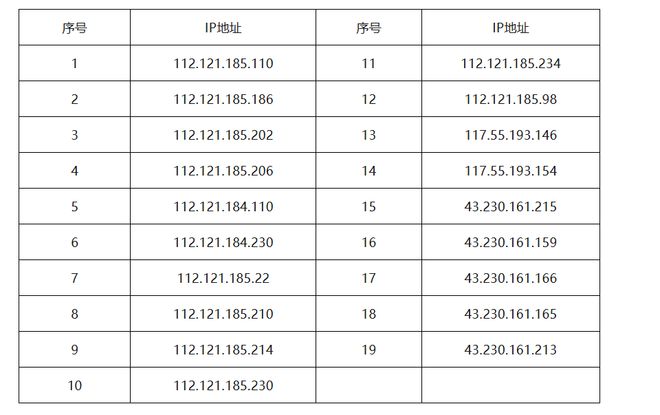
3. Some malicious IP addresses pointed to after domain name tampering
4. Prevention suggestions
It is recommended that relevant countries and units around the world strengthen risk awareness, carry out timely investigation and disposal, and focus on the following prevention work:
Regional Internet registration agencies, IP address trading platforms and other Internet number resource-related institutions should promptly verify and cancel malicious AS resources such as AS 402425.
Network operators should configure route filtering policies on border routing devices, verify route announcements, and reject and delete malicious routes containing AS 402425.
Internet platforms should strengthen monitoring of changes in core business domain name resolution IPs, abnormalities in DNS response messages, abnormal changes in routing paths, etc., to detect hijacking behaviors in a timely manner. Once a hijacking event is confirmed, report it to the upstream operator in a timely manner, requesting that the abnormal routing announcement be handled and the hijacking link be cut off.
It is recommended that the majority of Internet users strengthen their risk awareness, strengthen security precautions, and avoid unnecessary economic losses, including:
Use a verified and trusted public DNS service and avoid using DNS services from unknown sources.
When a page jumps to a malicious website, do not click any buttons or links on the page, do not download the programs provided by the page, close the page immediately, and clear the browser cache in a timely manner.
Keep the terminal operating system and browser updated to the latest version, enable system security protection software, and prevent malicious scripts, phishing and other attacks attached to jump pages.
Comments