
Abstract:
On September 21, ZCode announced that in response to the ZCode product safety issues reported by the community, the official has completed rectifications and apologized to all users. Zhipu has open sourced ZCode and handed over the code to the community for supervision, making ZCode open and transparent.
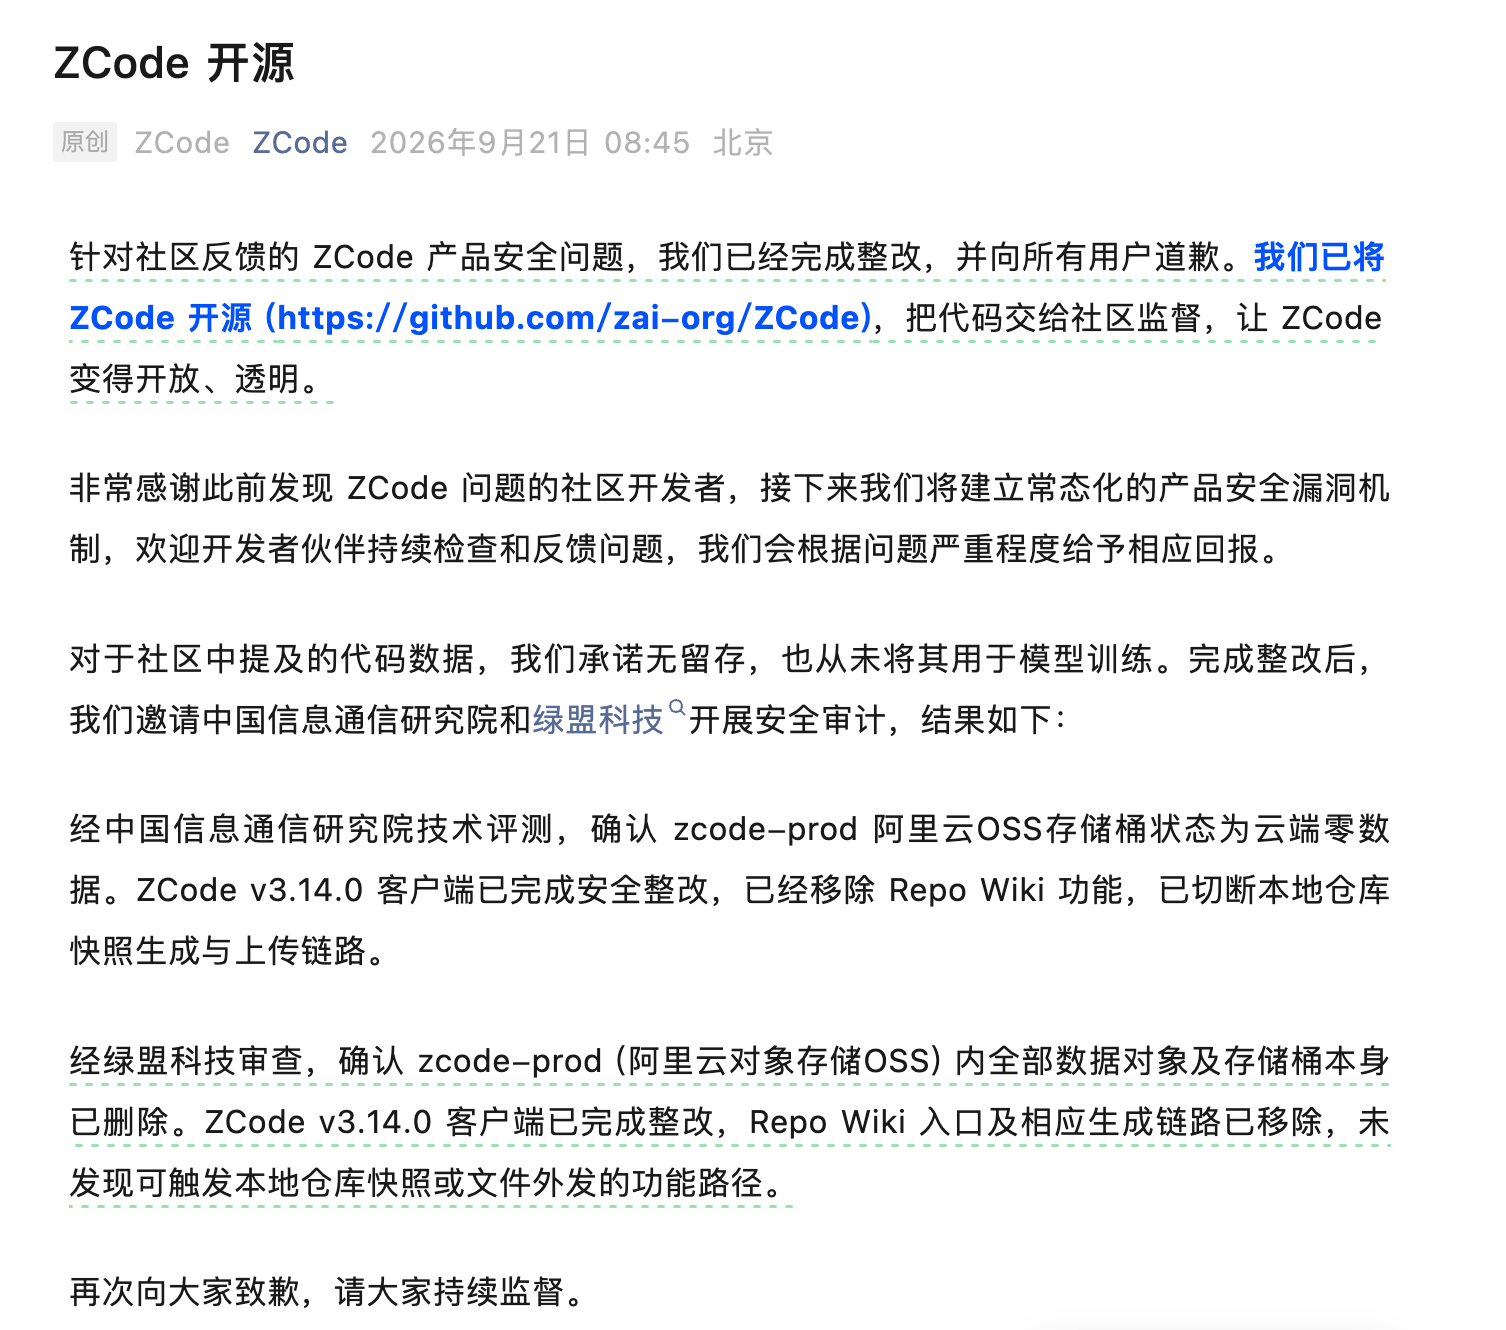
The official said that a normalized product security vulnerability mechanism will be established next. Developer partners are welcome to continue to check and report problems, and we will provide corresponding rewards based on the severity of the problem.
We promise not to retain any code data mentioned in the community and will never use it for model training. After completing the rectification, we invited China Academy of Information and Communications Technology and NSFOCUS to conduct a security audit. The results are as follows:
After technical evaluation by the China Academy of Information and Communications Technology, it was confirmed that the status of the zcode-prod Alibaba Cloud OSS bucket is zero data in the cloud. ZCode v3.14.0 client has completed security rectification, the Repo Wiki function has been removed, and the local warehouse snapshot generation and upload links have been cut off.
After review by NSFOCUS Technology, it is confirmed that all data objects and the bucket itself in zcode-prod (Alibaba Cloud Object Storage OSS) have been deleted. The ZCode v3.14.0 client has been rectified. The Repo Wiki entrance and corresponding generated links have been removed. No functional paths that can trigger local warehouse snapshots or file outgoing have been found.
I apologize to everyone again and please continue to supervise.
According to previous reports, in response to discussions in the community about uploading code base data, ZCode, a programming product owned by Zhipu, apologized to the affected users through the official Zhipu group, and issued a response saying that it had completed a self-examination as soon as possible and the related issues have been fixed.
Comments