
Abstract:
Google recently issued an announcement announcing adjustments to the Chrome Vulnerability Reward Program VRP. The new rules were announced to take effect immediately, encouraging security researchers to find vulnerabilities for memory corruption issues in Google browsers. With this update, the base reward for memory corruption vulnerabilities is increased from a minimum of $500 to $2,000, while proven controlled write vulnerabilities in browser, network, and GPU processes can earn up to $20,000.
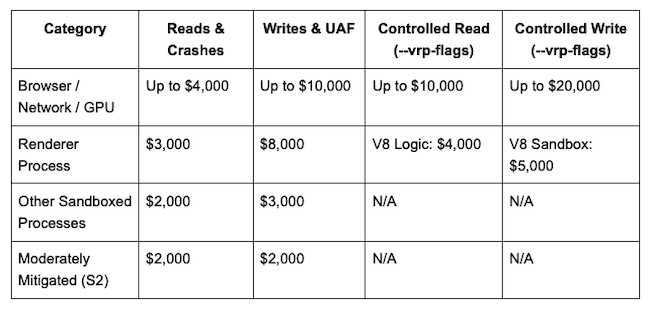
Reward amounts are graded according to vulnerability type and impact:
Vulnerabilities in the browser, network, and GPU processes are worth up to $4,000 for read or crash bugs, $10,000 for write and use-after-free bugs, $10,000 for controlled reads, and $20,000 for controlled writes.
Write and use-after-free vulnerabilities in the renderer process carry a maximum bounty of $8,000, V8 engine sandbox vulnerabilities are both $5,000, and V8 engine logic vulnerabilities are $4,000. Other sandbox-protected processes are worth $2,000 for read or crash bugs and $3,000 for write and use-after-free bugs.
Google also requires that the memory safety report must be reproducible on Google's infrastructure. If there is no report for the applicable test environment, the reward amount may be limited to the basic reward. Google said this requirement is mainly to match rewards with vulnerabilities that are reproducible and have a greater actual impact.
Added mid-risk bonus and restored Fuzzer bonus:
The Chrome VRP program has also added a new non-memory security vulnerability reward. S2 medium-risk issues can receive a $2,000 reward if the report contains a fix or directly contributes to the fix. If it is a non-memory security sandbox escape vulnerability with a large impact, a reward of up to US$20,000 will be provided.
Google also reinstated the $2,000 Chrome Fuzzer Bonus to reward security researchers who develop and contribute new fuzz testers. Google has also added new annual community awards, such as Best Report and Best Vulnerability. Google said that as its internal AI vulnerability detection capabilities improve, the reward program is adjusting its direction to encourage security researchers to find problems that are difficult to find with automated tools.
Comments