
Abstract:
Broadcom recently announced that its virtualization product VMware will release software security updates on a monthly basis. The main reason for this adjustment is that more and more product defects are discovered with the help of artificial intelligence technology, so Broadcom needs to release software updates faster to fix functional defects and security vulnerabilities.
However, increased update frequency will also require users to invest more time and energy in testing the impact of security updates on the existing environment. Some security updates that require downtime for updates may also cause more frequent service interruptions. However, based on security considerations, IT administrators must also install updates in a timely manner.
Introducing HyperArmor value-added services that require additional payment:
The service provides virtual patches to block exploit attempts for known vulnerabilities; changes to the ESX hypervisor in VMware Cloud Foundation allow the response policy to be updated only with administrator approval; ESX's SSH login can enable multi-factor authentication, requiring in addition to SSH credentials a dynamic verification code bound to a separate identity to connect properly.
This service will be provided as a paid add-on product of VMware Cloud Foundation, so multi-factor authentication functions such as SSH login also require additional money to activate value-added services before they can be used.
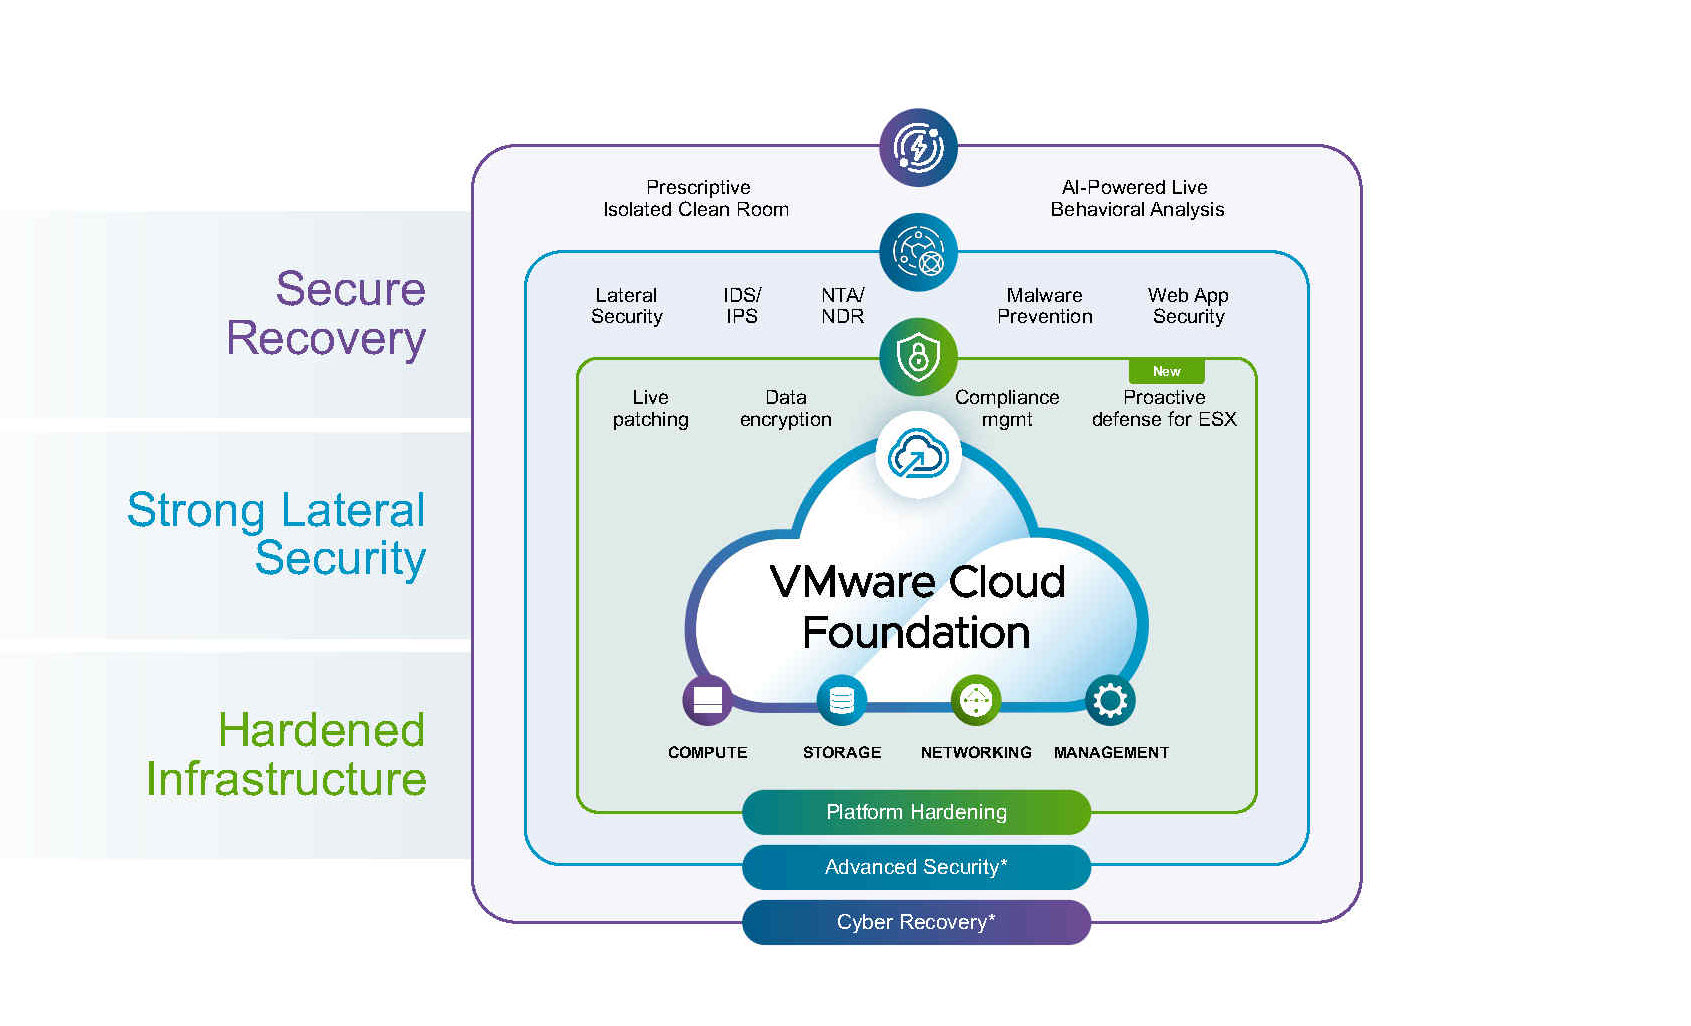
Value-added services are additional security measures:
The vice president of product marketing for VMware Cloud Foundation emphasized that even with real-time vulnerability fixes, customers need time to evaluate the impact of updates on their existing environments, and HyperArmor can add additional security protection during this time. However, this service is not a patch management tool, so it does not mean that you can skip software updates and normal testing processes after purchasing this service.
Comments