
Abstract:
Semiconductor giant Intel recently announced that it has officially terminated its long-running "Bug Bounty" cybersecurity vulnerability bounty program. Under the program's previous reward structure, external security researchers and white hat hackers could receive cash rewards of up to $100,000 for discovering and privately reporting high-risk security vulnerabilities in Intel hardware, firmware, or critical software. This strategic adjustment marks a major shift in Intel's security vulnerability collection and security community cooperation model.
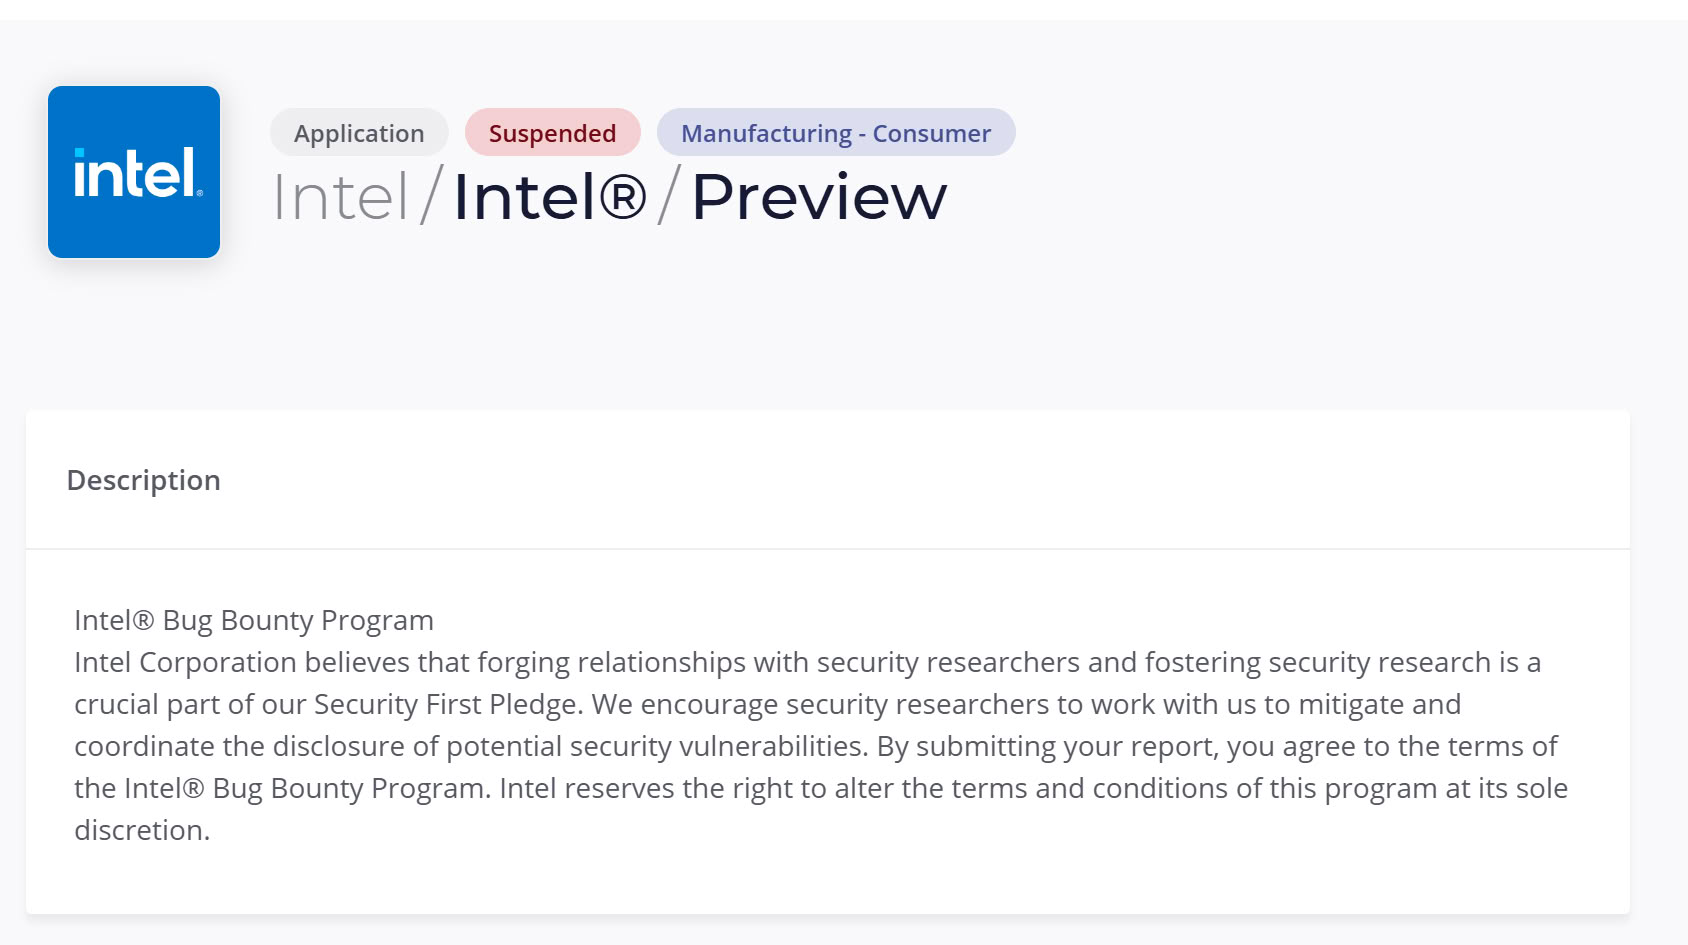
As the world's major chip manufacturer, Intel's bug bounty program has played a pivotal role in the past few years. Especially after a series of hardware-level predictive execution and side-channel attack vulnerabilities such as Specter and Meltdown attracted global attention, this program has become a key line of defense for Intel to attract the world's top security experts to help troubleshoot potential vulnerabilities and prevent zero-day attacks. However, as global cybersecurity compliance requirements evolve and the company's internal security strategies are reimagined, Intel has decided to end this high cash reward model.
Although it has terminated the Bug Bounty program for the public and independent researchers, Intel emphasized that this does not mean that it is relaxing its product security defenses. Intel said that in the future, the company will rely more heavily on its own large internal security research and development team, while deepening targeted security testing cooperation with specific trusted third-party security agencies, academic partners, and industry alliances. In addition, Intel will still maintain a compliant coordinated disclosure channel for vulnerability reports submitted by researchers, but it will no longer automatically promise to match the previous high financial rewards.
The cybersecurity industry has had mixed reactions to Intel's decision. The lack of direct financial incentives may reduce the enthusiasm of independent hackers to directly report vulnerabilities to manufacturers, and may even cause some undisclosed vulnerabilities to be transferred to the black market. However, some analysts believe that in the face of increasingly complex chip architectures, relying on general public bounties is no longer able to deal with deep technical risks. Shifting budgets to establish more systematic pre-security reviews and targeted cooperation may be an inevitable choice for chip manufacturers under current cost and efficiency considerations.
Comments