
Abstract:
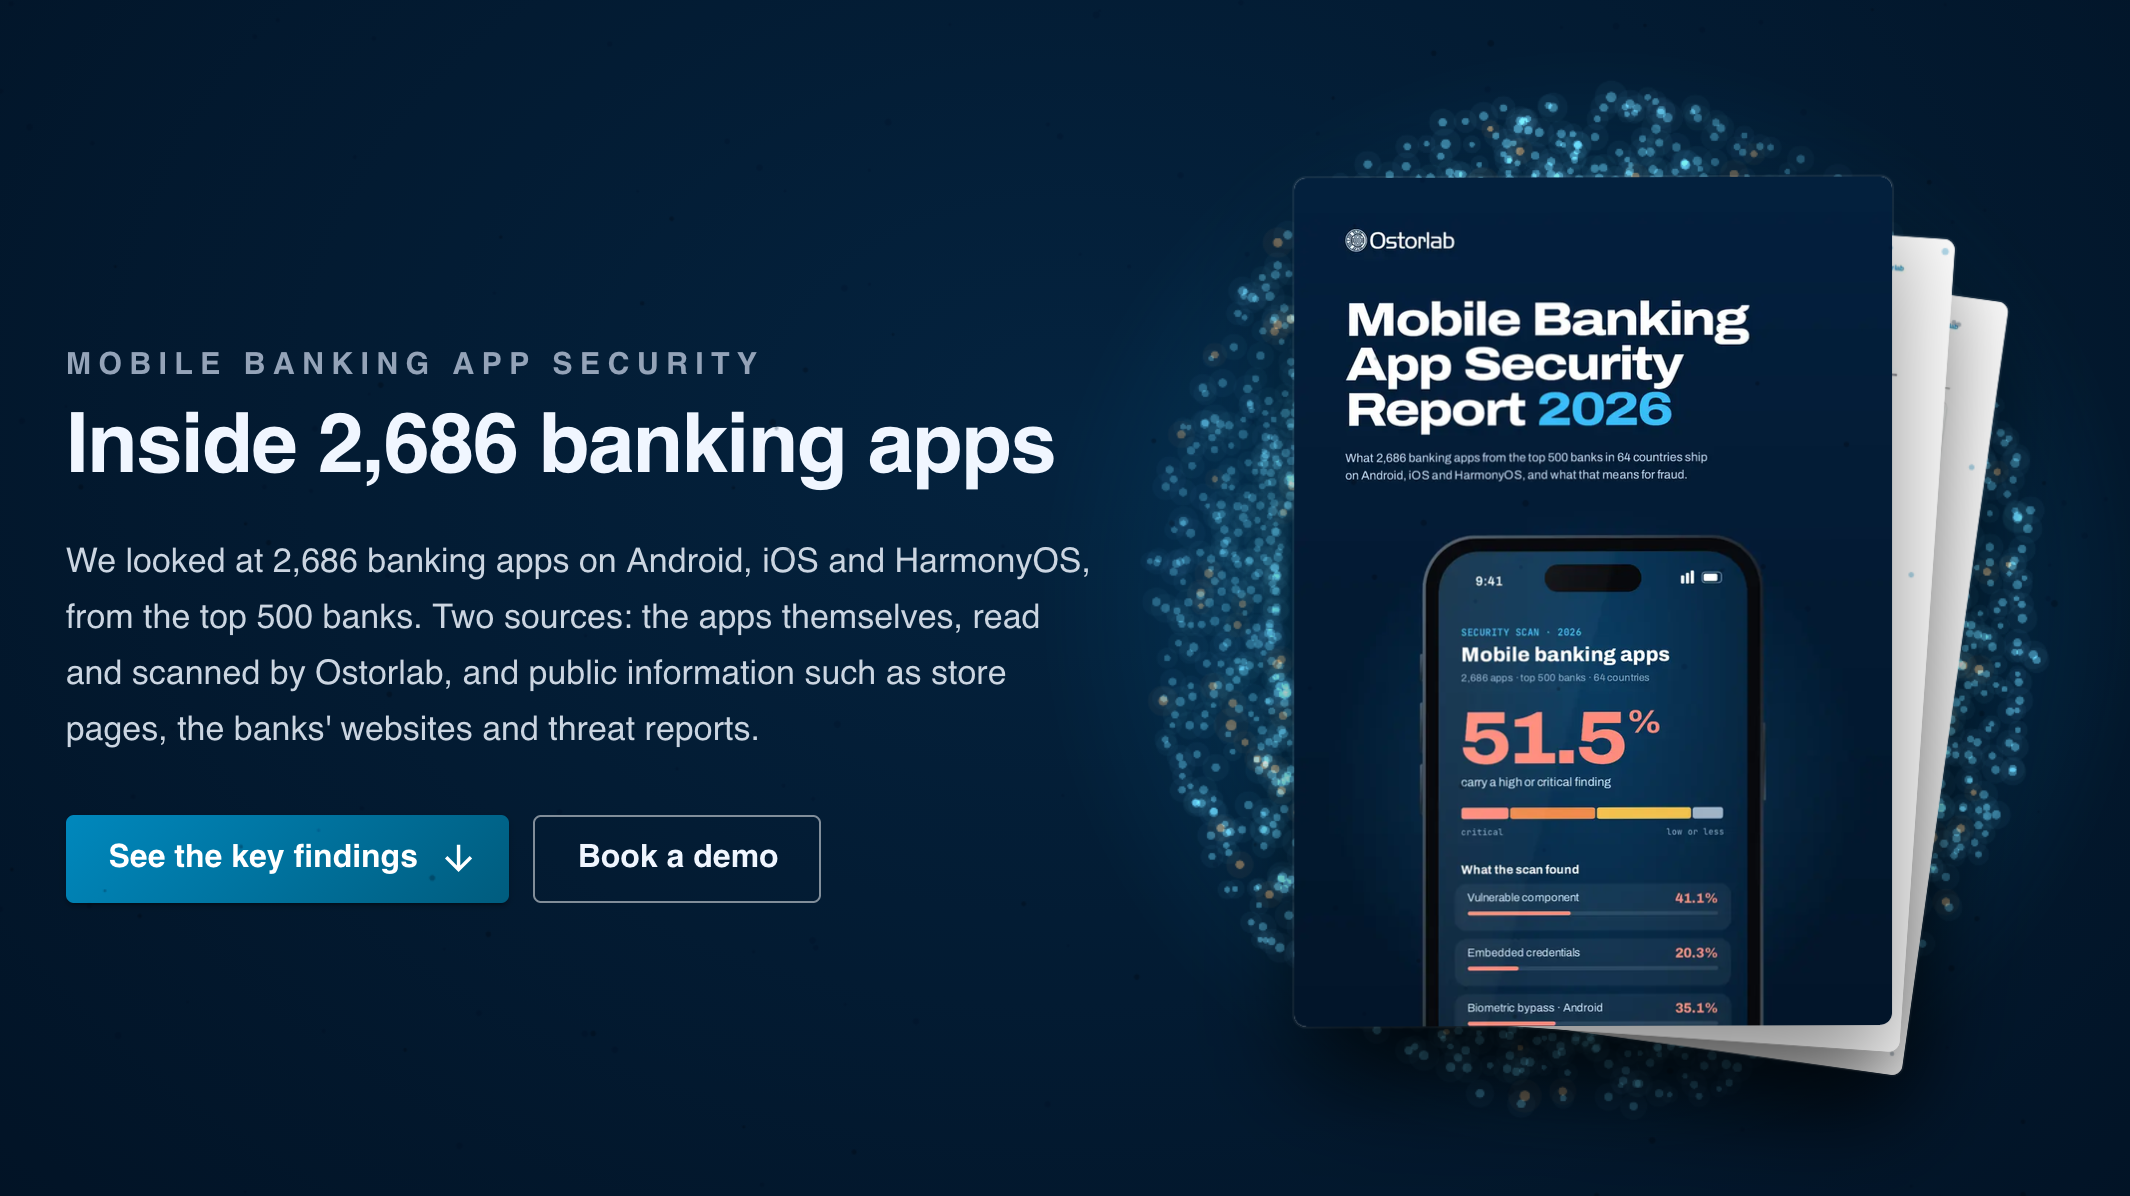
Network security agency Ostorlab released the "2026 Mobile Banking Application Security Report". This is the first time that Huawei's HarmonyOS has been included in the assessment scope of this annual report. This study analyzed a total of 2,686 mobile banking apps from 487 banks in 64 countries around the world, of which 478 were from Huawei App Gallery (AppGallery).
The evaluation results show that among the three major platforms of Android, iOS and HarmonyOS, the security risks of the Harmony platform are the most prominent. Data shows that 31.6% of Hongmeng Bank apps contain at least one critical level security flaw, which is not only the highest proportion among the three major platforms, but also much higher than the 18.4% average of all apps.
In terms of third-party component security, 56.7% of Hongmeng Bank apps integrate third-party components with disclosed vulnerabilities. This compares to 37.7% on Android and 37.4% on iOS. Ostorlab pointed out that the main reason for this gap is that many Hongmeng Apps are early ported versions that are packaged and use older third-party libraries.
Looking at overall industry data, 51.5% of all bank apps tested had at least one high-risk or severe security issue. In addition, in terms of the popularity of modern authentication technology, only 4.9% of banking apps support the passkey function.
Ostorlab added in the report that this study only published summary statistics and did not name any specific bank or app, and no actual attacks were launched on any app during the research process. The discovery of a security flaw only means that there is a potential risk in the app, but it does not mean that the vulnerability has been successfully exploited.
Full text of the report:
https://ostorlab.co/annual-reports/mobile-banking-2026
Comments