
Abstract:
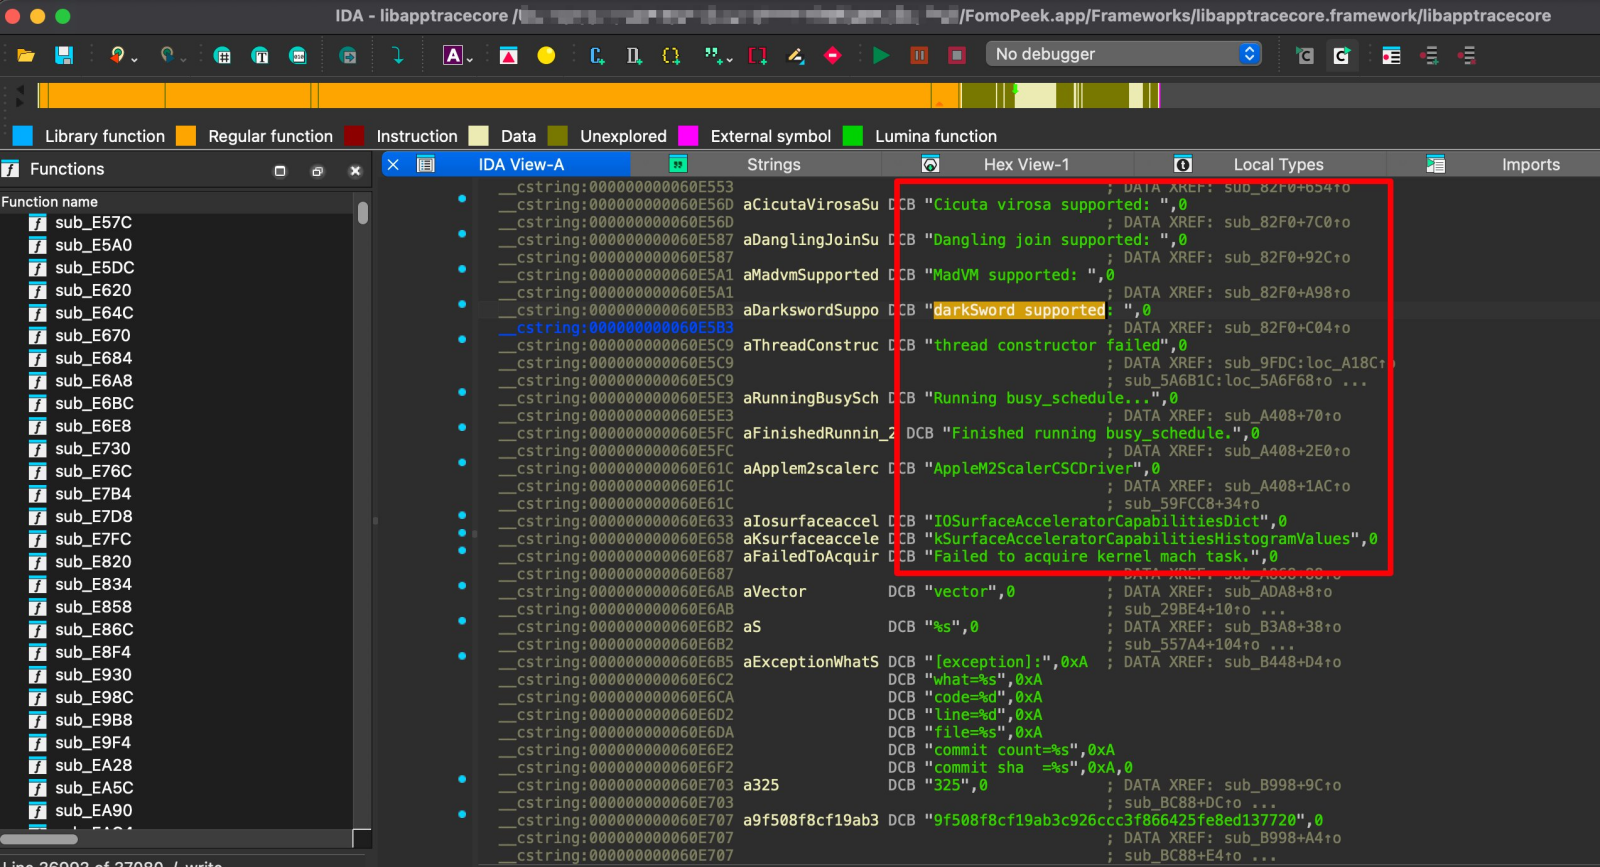
According to news released by security company SlowMist Technology, SlowMist has recently received multiple reports of user assets being stolen. Investigations found that the affected cases involved private key leaks, and these users have installed or have installed the FomoPeek application. FomoPeek itself is not a crypto wallet, but a tool that helps users pay attention to and track the movement of funds on the chain, and issues alerts to users when on-chain information that may affect the market occurs. However, the study found that the application has two built-in functional modules that have nothing to do with its declared business.
Built-in iOS kernel-level exploit framework used to steal information:
FomoPeek's built-in iOS kernel-level vulnerability exploitation framework has a variety of different exploitation methods. The framework can automatically select the attack method based on the device model and the actual iOS version used. A successful exploit could allow the attacker to escape the iOS sandbox and access and decrypt data in the keychain, as well as read files belonging to other apps on the device.
This means that all sensitive data stored on the device such as encrypted wallet private keys, mnemonic/seed phrases, login credentials, chat logs, files, etc. can be stolen by hackers and uploaded to attacker-controlled servers. FomoPeek can also remotely receive instructions from attackers.
This kernel-level vulnerability exploitation framework can launch attacks on iOS 12.0~iOS 18.7 and iOS 26.0~iOS 26.1, that is, using security vulnerabilities that Apple has fixed to launch attacks. If users always use the latest version of iOS, the vulnerabilities will be fixed and FomoPeek will not be able to continue to exploit the vulnerabilities.
Invite KOL to pay to attract new users to attract more users to download and install:
As a new project, FomoPeek cannot be quickly downloaded and used by more cryptocurrency users, so the application adopts a method of paying to invite KOLs to promote and attract new users. Pictures seen by Bluepoint.com show that KOL invites users to use the referral code to download and register the FomoPeek app, and then new users can receive a reward of 7USDT. As for KOLs, they may receive higher rewards.
In this way, FomoPeek can quickly contact a large number of users in the currency circle and induce users to download the application, and then begin to steal wallet private keys and transfer user assets. For cryptocurrency users whose assets were stolen, this wave of losses was very heavy. Many users’ wallets were directly emptied, and the assets were difficult to recover.
iOS remains safe as long as you always keep the latest version:
Judging from the current situation, these kernel-level attacks are likely to use the DarkSword series of exploit frameworks, which are high-risk iOS security vulnerabilities reported by Google in March 2026. After Google notified Apple, Apple has fixed the vulnerability in subsequent new versions, so users using the latest version are not affected.
Overall, the iOS system is still safe. The premise is that users should always use the latest version and turn on the automatic update function. Do not turn off updates completely because iOS becomes more and more stuck as it is updated. For users in the currency circle, using the latest version of iPhone+iOS has a higher safety factor. After all, it involves asset security issues, so safety is the priority.
In addition, attackers in the NodeSeek community earlier released a fake free VPS server activity. This activity also used the DarkSword series of attack frameworks, which means that this type of previously rare kernel-level attack has begun to attack ordinary users. Do not download applications from unknown sources and do not open unfamiliar websites are also defense methods, but in any case, you should keep iOS updated normally.
Comments