
Abstract:
Many network security agencies recently issued emergency warnings, pointing out that a new social engineering network attack method called "ClickFix" is spreading rapidly around the world. This attack method cleverly bypasses the traditional malicious file download and email attachment detection and killing mechanisms. By forging highly realistic system error pop-ups on mainstream websites, it induces Windows and Mac users to actively open system terminals and paste and execute malicious instructions, thereby achieving a covert intrusion that "allows the victim to hack his own device."
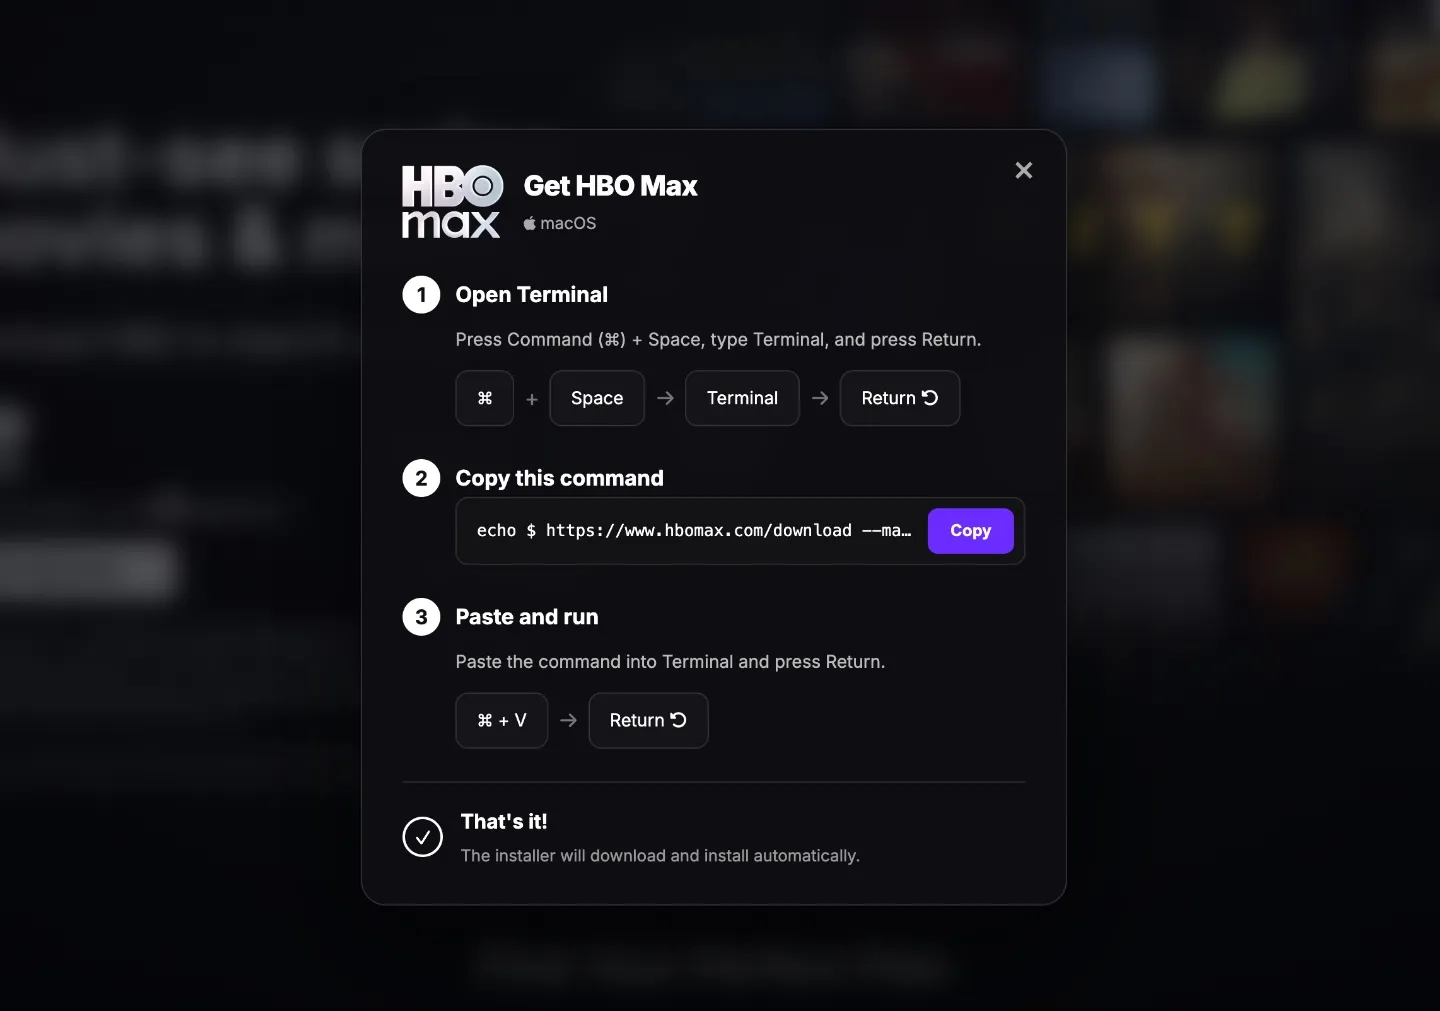
Unlike the traditional method of silently downloading virus files directly through fraudulent links, the core of the ClickFix attack is to exploit the victim's trust in common browser errors. Attackers usually first invade the advertising plug-ins of regular websites or inject malicious scripts. When users visit these tampered web pages, the page will suddenly pop up fake prompt boxes such as "Google Chrome has crashed", "Cloudflare human-computer authentication failed" or "System DNS resolution exception". In order to create the illusion of technical compliance, the pop-up window will claim that this is a routine problem that can be quickly repaired, and provide users with a set of so-called "one-click repair steps."
Once the victim is gullible and clicks the "Copy Code" button on the interface, a heavily obfuscated Base64 encoded script will be quietly written to the clipboard. Subsequently, the prompt box will step by step instruct Windows users to press the "Win + R" keys to evoke the run window and open PowerShell, or instruct Mac users to open the Terminal, paste the code directly and press Enter to execute. During the entire process, because the code is personally triggered by the user with the highest authority, most anti-virus software and default download protection strategies built into the operating system (such as macOS's Gatekeeper or Windows SmartScreen) often do not judge it as an external illegal download and are completely bypassed.
Security researchers analyzed that once these obfuscated commands are executed in the terminal, the system will silently connect to the remote server controlled by the attacker in the background, quickly download and deploy the secret-stealing Trojan (Infostealer). Attackers can use this to not only search for account passwords, cryptocurrency wallet keys, cross-session cookies and two-factor authentication tokens saved in the browser, but also to establish persistent backdoor access to the system, and even further penetrate the victim's local area network to deliver ransomware. What's even more serious is that with the evolution of cross-platform compatible attack tools, hacker groups have written customized AppleScript and Shell exploit chains for macOS, making the Mac ecosystem, which was considered relatively safe in the past, also facing serious threats.
In response to this new threat that relies heavily on psychological manipulation rather than traditional vulnerability exploitation, security experts emphasize that no formal technology company, browser developer or website verification service will require end users to manually open a system terminal or run a window to solve web browsing failures. Enterprise IT management departments should promptly configure terminal protection policies to limit the command line execution rights of non-administrator users. When individual users face any pop-up window claiming that "copying a script can fix network or browser errors", they should remain vigilant and close the web page immediately, and do not blindly execute instructions from unknown sources in the terminal.
Comments